VERDICT: The Central Bank of the UAE (CBUAE) has moved beyond Open Banking to Open Finance, mandating that financial data sharing extends to insurance and investment sectors.
MOTIVE: To position the UAE as a global digital finance hub by breaking down data silos, empowering consumers, and fostering competition through interoperable financial data.
FIX: Tech platforms acting as Third-Party Providers (TPPs) must secure specific CBUAE licenses for Account Information (AIS) or Payment Initiation (PIS) immediately or risk “Unlicensed Activity” penalties.
You might be wondering… why a software update in your banking app suddenly has legal consequences for your business.
My journey began writing C code on UNIX systems. Back then, we understood that an API (Application Programming Interface) was just a bridge between two machines. Today, in the UAE’s new financial ecosystem, an API is a bridge between legal liabilities. As Adv. Shoeb Hakim, having led Anti-Money Laundering (AML) strategies at Credit Suisse, I see the Open Finance mandate not just as a technical upgrade, but as a shift in the concept of “ownership.”
The CBUAE is essentially saying that customer data no longer belongs to the bank; it belongs to the customer. However, if your technology platform facilitates the movement of this data, you are no longer just a tech vendor. You are a regulated financial entity. The “pipe” is now as regulated as the “water” flowing through it.
The New Architecture of Trust: AIS and PIS
The regulation categorizes Third-Party Providers (TPPs) into two distinct buckets. Understanding this distinction is critical for your compliance strategy.
1. Account Information Services (AIS) This allows a platform to aggregate data. If your app shows a user their bank balance, credit card limit, and insurance policy in one dashboard, you are an AIS provider. You are “reading” the ledger.
2. Payment Initiation Services (PIS) This allows a platform to execute transactions. If your app allows a user to pay their utility bill directly from their bank account without leaving your interface, you are a PIS provider. You are “writing” to the ledger.
Visual Insight Cards: The Liability Matrix
⚠️ The Risk ➔ “Just a Tech Vendor” Fallacy
Stakeholder: Fintech Startups / SaaS Platforms.
Action: If you touch the data or trigger the payment, you need a license. Claiming to be a “software provider” is no longer a defense against CBUAE fines.
🔐 The Gatekeeper ➔ Consent Architecture
Stakeholder: Compliance Officers.
Action: Consent must be “Explicit, Granular, and Revocable.” A generic Terms of Service checkbox does not satisfy the Open Finance regulatory standard.
🛡️ The Shield ➔ API Security Standards
Stakeholder: CTOs and Legal Heads.
Action: Security is now a legal mandate. A data breach is not just an IT failure; it is a regulatory violation under the Consumer Protection Regulation.
The “UNIX” Perspective on Data Sovereignty
In the UNIX world, permissions are binary—read, write, execute. The CBUAE has applied this logic to finance. The new framework demands Interoperability with Consent.
This means your infrastructure must be robust enough to “talk” to every bank in the UAE, but secure enough to “listen” only when the customer says so. As a Visiting Faculty to the Maharashtra Police, I teach that digital trails are permanent. In Open Finance, every API call is a legal record. If you access data without a valid, time-stamped consent token, you are technically committing data theft under the Cybercrime Law.
The era of “screen scraping”—where apps would log in as the user to get data—is dead. It is insecure and now illegal. You must integrate through the official, regulated Open Finance APIs.
Conclusion: The Compliance Roadmap
The transition period is tight. The CBUAE is moving fast to implement this framework. If you operate a digital platform in Dubai that interacts with financial data, you must conduct a Licensing Gap Analysis immediately.
Do not wait for a regulatory notice. In the world of Open Finance, visibility is total. If you are operating without a license, the regulator can see you in the API logs.
Metadata Output:
File Name: open-finance-dubai-legal-framework-adv-shoeb-hakim.webp
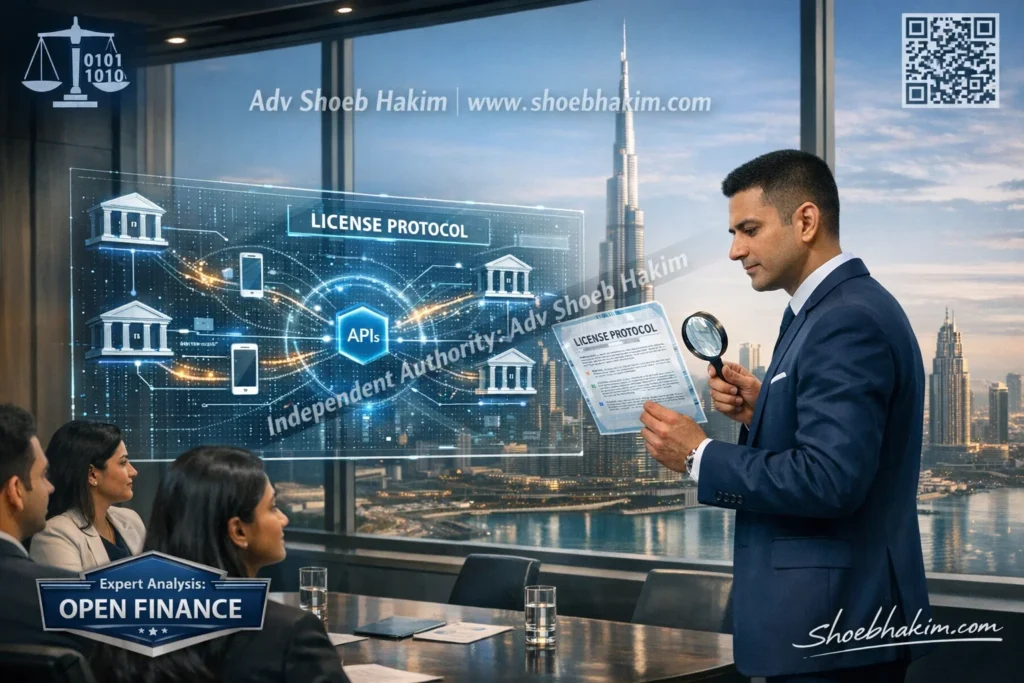
Alt Text: “Adv Shoeb Hakim analyzing Open Finance Dubai legal framework and API data sharing mandates for fintech compliance.”
Title Text: Open Finance Dubai Legal Framework Analysis
Caption: “Data sharing requires strict licensing under CBUAE mandates. | Source: shoebhakim.com”
Description: “Adv Shoeb Hakim explains the legal implications of the Open Finance mandate in Dubai, focusing on AIS and PIS licensing requirements.”
Quiz
Question 1: What is the primary difference between Account Information Services (AIS) and Payment Initiation Services (PIS)?
A) AIS handles cash; PIS handles checks
B) AIS is for reading data; PIS is for executing transactions
C) AIS is for insurance; PIS is for banking
Question 2: Under the CBUAE Open Finance mandate, who ultimately owns the financial data?
A) The Bank
B) The Customer
C) The Technology Provider
Question 3: What type of consent is required for Third-Party Providers to access user data?
A) Implicit Consent
B) General Terms & Conditions
C) Explicit, Granular, and Revocable Consent
Question 4: Under the Bharatiya Sakshya Adhiniyam (BSA), 2023, which section governs the admissibility of electronic records (such as API logs)?
A) Section 45
B) Section 61
C) Section 63
Answer Key: 1(B), 2(B), 3(C), 4(C).

⚠️ Professional Disclaimer
Educational Purpose Only: The content provided (including references to BNS, BSA, and RBI/IRDAI circulars) is for educational purposes only. It is not legal or investment advice.
No Client Relationship: Accessing this information does not create an Advocate-Client relationship with Adv. Shoeb Hakim.
Supremacy of Law: We respect the Constitution of India. All critiques are constructive suggestions for systemic improvement, not confrontation with government entities.
Cyber Fraud Emergency: Dial 1930 immediately to report financial fraud on the National Cyber Crime Portal.
Advertisement
Focus Keyphrase: Open Finance Dubai Legal Framework
SEO Title: Open Finance Dubai Legal Framework: CBUAE Guide | Adv Shoeb Hakim
Slug: open-finance-dubai-legal-framework-adv-shoeb-hakim
Meta Description: “You might be wondering if your app needs a license. Adv Shoeb Hakim explains the Open Finance Dubai Legal Framework and CBUAE data sharing rules.”
Serial Number: SHOEBHAKIM/01/03/19012026/019/ADVSHOART+F5K3J8R
Hashtags: #advshoebhakim #shoebhakim #advshoaibhakim #OpenFinance #DubaiFintech #CBUAE #LegalTech #DataPrivacy #OpenBanking #FintechLaw #Compliance #DigitalEconomy #SmartDubai #TechnoLegal #FinancialRegulation #AIS #PIS #UAEBusiness #CyberLaw #DigitalSovereignty #ShoaibHakim #APIsecurity #DataSharing #FutureOfFinance #BankingLaw #RegulatoryCompliance #FintechStartups #MiddleEastTech