Cybercriminals cast a wide net, but certain groups and sectors are more frequently targeted due to the value of their data or perceived vulnerabilities. Here are some of the most commonly targeted groups:
Most Targeted Groups by Cybercrime
- Healthcare Sector
- Why: Healthcare organizations hold sensitive patient data, making them prime targets for ransomware attacks and data breaches.
- Impact: Disruption of healthcare services, theft of confidential patient records, and financial losses.
- Financial Institutions
- Why: Banks and financial institutions handle large volumes of money and sensitive financial information, attracting cybercriminals looking for financial gain.
- Impact: Fraud, theft of funds, and compromised customer data.
- Critical Infrastructure
- Why: Sectors like energy, telecommunications, and transportation are essential for national security and public safety, making them targets for state-sponsored attacks and cyberterrorism.
- Impact: Disruption of essential services, potential national security threats.
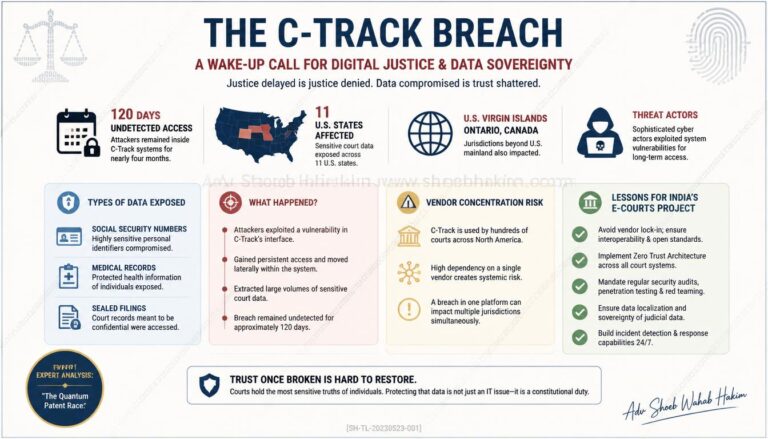
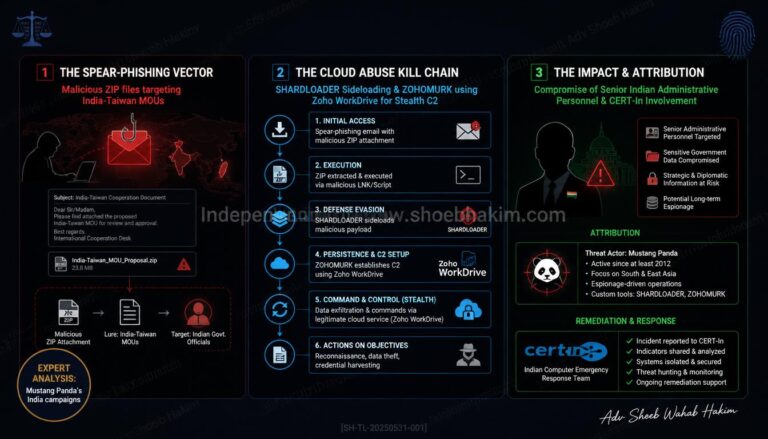
- Government and State Institutions
- Why: Government agencies hold valuable data and are often targeted for espionage, political gain, or disruption of public services.
- Impact: Data breaches, espionage, and disruption of government operations.
- Small and Medium-Sized Enterprises (SMEs)
- Why: SMEs often lack robust cybersecurity measures, making them easier targets for cybercriminals.
- Impact: Financial losses, data breaches, and business disruption.
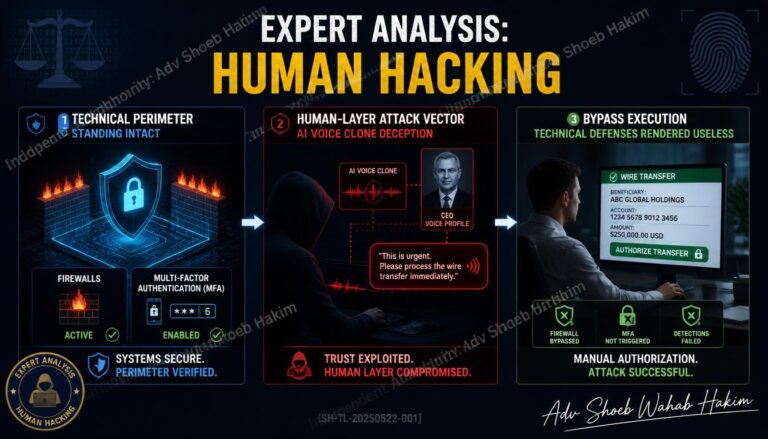
- Individuals
- Why: Individuals are targeted through phishing, identity theft, and social engineering attacks due to the personal information they possess.
- Impact: Financial loss, identity theft, and compromised personal data.
Statistics on Cybercrime Impact
- Healthcare Sector: Accounts for 14.2% of all cyberattacks targeting critical infrastructure.
- Financial Institutions: Account for 8.3% of attacks on critical infrastructure.
- Critical Infrastructure: Experienced 500 incidents involving sectors like energy, telecommunications, and transport in 2023 alone.
Best Practices for Protection
- Implement Robust Cybersecurity Measures
- Use firewalls, antivirus software, and intrusion detection systems.
- Regularly update and patch systems to fix vulnerabilities.
- Employee Training and Awareness
- Conduct regular cybersecurity training sessions for employees.
- Educate staff on recognizing phishing attempts and social engineering tactics.
- Data Encryption and Backup
- Encrypt sensitive data to protect it from unauthorized access.
- Regularly back up data to ensure recovery in case of a cyberattack.
- Access Controls
- Implement strict access controls to limit who can access sensitive information.
- Use multi-factor authentication to enhance security.
By understanding who is most likely to be targeted and implementing best practices, organizations and individuals can better protect themselves against cybercrime.