By Shoeb Hakim
Introduction
Artificial intelligence in anti-money laundering has reached a decisive moment. Regulators, banks, and vendors are no longer debating whether AI belongs in financial crime compliance. The question is which jurisdiction will define the rules first—and whether your institution can produce the evidence they will demand.
Napier AI’s recent analysis identifies three regulatory postures. The UK and France are “AI accelerators,” with sandboxes and risk-based supervision. The US, EU, and Singapore are “AI appreciators,” enthusiastic but working through fragmented rulebooks. Australia, Canada, and the UAE are “AI appraisers,” prioritising auditability and explainability over speed. Paradoxically, this caution may result in them setting the toughest global standard.
But for Indian financial institutions, the most immediate regulatory signal is not coming from Brussels or Canberra. It is coming from Mumbai.
The 40-Word Answer: What is the legal risk of deploying AI in AML without explainability?
Under the Reserve Bank of India’s Draft Guidance on Model Risk Management (June 2026), regulated entities are fully accountable for third-party AI model outcomes. The guidance mandates explainability, bias testing, hallucination controls, and human oversight. Failure to produce audit-ready evidence exposes the board to supervisory action.
Part 1: The RBI’s Model Risk Management Mandate
The Reserve Bank of India released its Draft Guidance on Regulatory Principles for Model Risk Management in June 2026. The scope is broad. It applies to banks, NBFCs, AIFIs, ARCs, and credit information companies. It covers statistical, mathematical, and AI/ML models, whether developed internally or sourced from third parties.
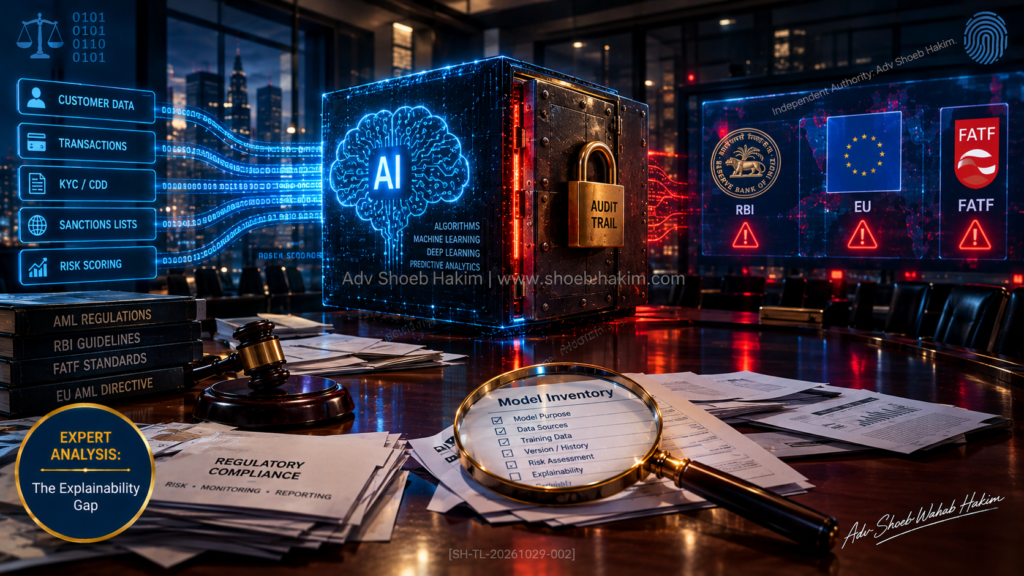
The requirements are specific. High-risk models require independent validation and Risk Management Committee approval before deployment. No model may be used unless it is included in a mandatory model inventory. The guidance introduces AI/ML-specific requirements covering explainability, bias and fairness testing, hallucination controls, drift monitoring, and human oversight. Crucially, the RBI holds regulated entities fully accountable for third-party model outcomes and requires independent validation regardless of vendor assurance.
This is not a future obligation. The guidance is open for consultation and, once finalised, will replace Chapter 3 of the RBI’s 2002 Guidance Note on Credit Risk Management. Institutions that are deploying AI for transaction monitoring or customer risk scoring today are building on a framework that the regulator has already signalled is insufficient.
Part 2: The EU AI Act and the Global Divergence
The European Union’s AI Act adds another layer of complexity. Transaction monitoring, KYC, and sanctions screening are widely treated as high-risk AI use cases when AI is deployed. The Act mandates transparency, human oversight, data governance, and lifecycle management.
But the timeline is not as uniform as vendor commentary suggests. The high-risk obligations under Annex III, which carry the detailed risk management and human oversight requirements, now apply from 2 December 2027, not August 2026, following the AI Omnibus simplification package. Separately, Annex III’s only explicitly named financial services category, covering creditworthiness evaluation, expressly excludes fraud detection. AML transaction monitoring is not named anywhere in Annex III’s list at all.
This does not mean the AI Act is irrelevant. Transparency obligations under Article 50, covering disclosure when a person is interacting with an AI system, came into effect on 2 August 2026. But the divergence between jurisdictions is real. The UK and France are accelerating. The EU is clarifying and delaying. Australia and Canada are prioritising auditability. India is consulting on a model risk framework that is more prescriptive than any of them on third-party accountability.
For an Indian bank with European operations, the compliance burden is a patchwork of overlapping and sometimes conflicting expectations.
Part 3: FATF’s Endorsement and the “Appropriate Safeguards” Condition
The Financial Action Task Force has formally endorsed the use of AI in financial crime compliance. Paragraph 13 of the FATF Ministerial Declaration, signed in April 2026, endorses AI “with appropriate safeguards.”
That phrase is doing a lot of work. The FATF is not endorsing AI for its own sake. It is endorsing AI paired with explainability, accountability, and audit trails that an institution can produce on demand. Most financial institutions are deploying AI tools in transaction monitoring and client screening without documentation that would survive an examination. The ministers have drawn a line. The question is whether your institution is on the right side of it.
Part 4: The Agentic AI Distraction
Napier AI’s analysis is sceptical of agentic AI as a standalone answer. An agent that triages alerts faster without improving detection quality simply moves the same risk around more efficiently, while adding another layer that must be explainable, auditable, and free of hallucination.
The model regulators will trust is different: AI built around embedded, jurisdiction-specific risk intelligence, informed by shared typology knowledge, and subject to continuous validation. This is harder to build than a workflow layer. It is also the only AI in AML that survives sustained regulatory scrutiny rather than a single audit cycle.
Part 5: The Explainability Audit
To bridge the gap between AI adoption and regulatory defensibility, I use a proprietary 3-Phase Explainability Audit for financial institutions and their boards.
Phase 1: The Model Inventory and Risk Tiering Review.
We map every AI and ML model used in your AML and transaction monitoring stack against the RBI’s draft MRM requirements. We identify which models qualify as high-risk and whether they have undergone independent validation.
Phase 2: The Explainability Stress Test.
We take a sample of AI-generated alerts and risk scores and attempt to reconstruct the decision path. If a regulator asked your team to explain why a specific transaction was flagged or cleared, could they produce a defensible audit trail? We document the gaps and design the remediation.
Phase 3: The Third-Party Accountability Shield.
We review your vendor contracts and model documentation to ensure that, in the event of a supervisory inquiry, your institution can demonstrate independent oversight of third-party models. The RBI’s guidance holds you accountable for vendor outcomes. The contract must reflect that.
Conclusion
AI in AML is moving from experimentation to regulatory endorsement to expectation. The winners will not be the institutions with the most complex models. They will be the ones whose AI is built to align with how regulators define acceptable, explainable artificial intelligence. That is a compliance-first design principle, not a technology one. And it is why getting the foundations right matters more than moving fastest.
Key Takeaways
- The RBI’s draft MRM guidance makes boards accountable. Regulated entities are fully responsible for third-party AI models and must ensure explainability, bias testing, and human oversight.
- The EU AI Act’s high-risk deadline has moved to December 2027. AML transaction monitoring is not explicitly named in Annex III, but transparency obligations are already in force.
- FATF endorses AI only with “appropriate safeguards.” Explainability, auditability, and on-demand evidence are the conditions.
- Agentic AI is not a silver bullet. Faster triage without better detection just moves risk around. Regulators want evidence of model quality, not workflow automation.
- The window to build governance is now. Institutions in fast-follower markets should import proven approaches and strengthen documentation before the bar rises.
Adv Shoeb Hakim is a legal professional specialising in AML, cybercrime, digital forensics, and banking regulation. The views expressed are personal.
#advshoebhakim #shoebhakim #AML #PMLA #DPDPAct #AIGovernance #advshoebhakim #shoebhakim #shoiabhakim #hakimshoeb #advshoiabhakim #advshoebh #ModelRiskManagement #RBI #FATF #BankingRegulation #DigitalForensics #LegalCompliance #ArtificialIntelligence #AntiMoneyLaundering #FinancialCompliance #RegulatoryFramework #ModelRiskManagement #Explainability #BiasTesting #HumanOversight #AIinFinance #RBI #FinancialInstitutions #AMLCompliance #RiskManagement #AIRegulations #FinancialCrime #DataGovernance #ComplianceStandards #AIModels #AuditReady #FinancialTechnology