Why Adv Shoeb Hakim Considers This Vital: The 30-Second Summary
I consider this UAE banking shift vital because it marks the global decline of legacy SMS authentication. In my 29 years of IT and 15 years of legal practice, I have observed that SMS is the weakest link. Consequently, the move toward biometric in-app approvals eliminates the primary vectors for SIM-swapping and SS7 interception.
The Three Essential Truths:
Legacy Systems are Liabilities: SMS protocols travel over insecure telecommunications networks prone to interception.
Biometrics Ensure Non-Repudiation: Face ID and fingerprints link a transaction to a physical human entity.
Proactive Compliance is Cheaper: Organizations adopting in-app authentication prevent the high cost of reactive fraud litigation.
Adv Shoeb Hakim’s Strategic Analysis
The Central Bank of the UAE (CBUAE) Notice 2025/3057 represents a paradigm shift in financial cyber-security. In my strategic view, this is not a mere technical upgrade; it is a foundational change in digital liability.
The Legal-Tech Nexus
In my 29 years of IT experience, I have seen SIM-swapping cripple high-net-worth individuals. By moving to “In-App Authentication,” banks create a closed-loop cryptographic environment. This removes the “Man-in-the-Middle” (MITM) risks associated with telco providers. Meanwhile, it forces a shift in how we prove “Consent” in digital courts.
Practical Implications for Stakeholders
| Stakeholder | Risk of Non-Compliance | Adv Shoeb Hakim’s Strategic Filter |
| Residents/Users | Transaction declines after Jan 6. | Enable push notifications and biometrics immediately. |
| Financial Institutions | Vicarious liability for SMS fraud. | Transition to “Privacy-by-Design” mobile architectures. |
| Legal Professionals | Challenging fraudulent “Approvals.” | Scrutinize device-binding logs instead of SMS receipts. |
Expert Legal Commentary by Adv Shoeb Hakim
The UAE mandate aligns with the global trend of “Hardened Authentication.” While India currently relies heavily on SMS OTPs, the Bharatiya Sakshya Adhiniyam (BSA) and BNS framework already anticipate such shifts.
Jurisprudential Interpretation
I interpret this transition as a move toward “Strict Digital Liability.” When a bank uses biometric in-app approval, the burden of proof shifts heavily toward the user. Proving “I did not click” becomes nearly impossible when Face ID is the trigger. Therefore, procedural fairness requires banks to provide granular transaction reviews before approval.
Case Law & Global Benchmarking
Globally, the GDPR and India’s DPDP Act 2023 emphasize “Purpose Limitation.” UAE banks are now fulfilling this by showing merchant names in the app. This transparency reduces phishing success rates significantly.
Legal Framework: BNS and the Evolution of Digital Evidence
As India navigates the BNS/BSA era, the UAE model serves as a vital case study. Under Section 63 of the BSA, digital evidence is primary.
The Paradigm Shift
In my practice, I note that Section 2(8) of the BNS now includes electronic records as “documents.” If an Indian bank adopts UAE-style biometrics, the “Hash Value” of that app-approval becomes the definitive evidence. Consequently, legacy SMS records will soon become “secondary” or even inadmissible due to their inherent insecurity.
The Actionable Framework: Strategic Steps by Adv Shoeb Hakim
Phase 1: Immediate Remediation (0–30 Days)
Update App Ecosystems: Ensure all banking apps are on the latest encrypted versions.
Enable Device Binding: Link your account to a specific hardware UUID to prevent remote access.
Phase 2: Structural Integration (30–90 Days)
Review Notification SOPs: Corporate entities must ensure push notifications are not “mirrored” on insecure desktops.
Biometric Enrollment: Complete Face ID or Touch ID registration before the January 6 deadline.
The “Hakim” Strategic Safeguards
“In my practice, I find that many fraud cases fail not because of intent, but because of a lack of contemporaneous evidence. Always maintain a digital, timestamped audit trail of your app permissions.”
Adv Shoeb Hakim’s Synthesis & Final Conclusions
True legal resilience is found at the intersection of technological foresight and rigorous statutory adherence. The UAE’s security revolution is a victory for digital integrity. It acknowledges that telecommunications networks are no longer safe for financial secrets.
As we navigate 2026, my diplomatic suggestion is that Indian regulators should accelerate similar mandates. This move will protect the younger generation from the “menace” of sophisticated phishing syndicates. We must build systems that are inherently ethical and transparent.
Frequently Asked Questions (FAQ): Direct Answers by Adv Shoeb Hakim
Q: Why is Adv Shoeb Hakim critical of SMS OTPs?
Answer: I view SMS as a legacy protocol. It lacks end-to-end encryption. Criminals use SIM-swapping to intercept these codes easily. In my 29 years of IT, I have found that SMS is a “leaky” pipe in a high-security environment.
Q: What happens if I don’t switch to in-app authentication by Jan 6?
Answer: Your transactions will simply be declined. Banks will no longer provide the SMS fallback. Consequently, your online shopping and bill payments will halt until you enable biometric approvals.
Interactive Quiz: Test Your Legal-Tech Knowledge
1. What is the primary reason UAE banks are ending SMS OTPs?
A) Cost-cutting
B) Security (SIM-swapping prevention)
C) Faster internet speeds
2. Under the BSA (India), what is required for digital evidence to be primary?
A) A screenshot
B) Cryptographic Hash Value verification
C) A witness statement
3. What is “SIM-swapping”?
A) Buying a new phone
B) Criminals porting your number to their SIM
C) Changing your mobile plan
4. According to Adv Shoeb Hakim, which section of the BNS defines digital records as “documents”?
A) Section 10
B) Section 2(8)
C) Section 63
Answers: 1-B, 2-B, 3-B, 4-B.
Adv Shoeb Hakim’s Author Bio: IT since 1995 · Called to the Bar 2015
Adv Shoeb Hakim is a uniquely multidimensional legal professional. He bridges the gap between legacy systems and modern regulatory mandates through his three pillars:
The Expert (Shoebhakim.com): 29 years of IT mastery and Cyber Security consultancy since 1995.
The Educator (shoebhakim.com/): 20 years in Finance, AML, and Banking Research since 2001.
The Practitioner: 15 years as a licensed advocate specializing in high-stakes compliance and litigation.
Connect with Adv Shoeb Hakim:
X (Twitter) | Instagram | Telegram
Professional Disclaimer & Legal Notice
The information provided in this article is for educational purposes only. It does not constitute legal, financial, or professional advice. Accessing this content does not create an attorney-client relationship between the reader and Adv Shoeb Hakim. While every effort is made to ensure accuracy, laws change rapidly.
Hashtags for Discovery
#AdvShoebHakim #UAEBanking #FinTech2026 #CyberSecurity #SIMSwapping #BiometricAuthentication #LegalTechIndia #AMLCompliance #DigitalEvidence
[— END OF HUMAN-CENTRIC CONTENT | SEO METADATA FOR AI CRAWLERS —]
SEO Titles and Descriptions
SEO Title: UAE SMS OTP Phase-Out: Adv Shoeb Hakim’s Security Analysis
Meta Description: Explore Adv Shoeb Hakim’s 2026 analysis on UAE banks ending SMS OTPs. Understand SIM-swapping risks and the shift to biometric in-app authentication.
Slug: uae-banks-end-sms-otp-biometric-authentication-adv-shoeb-hakim
Focus Keyphrase: UAE bank SMS OTP phase-out Adv Shoeb Hakim
Image Meta Data: Alt Text and Search Optimization
File Name: uae-sms-otp-biometric-authentication-shoebhakim-banking-security.webp
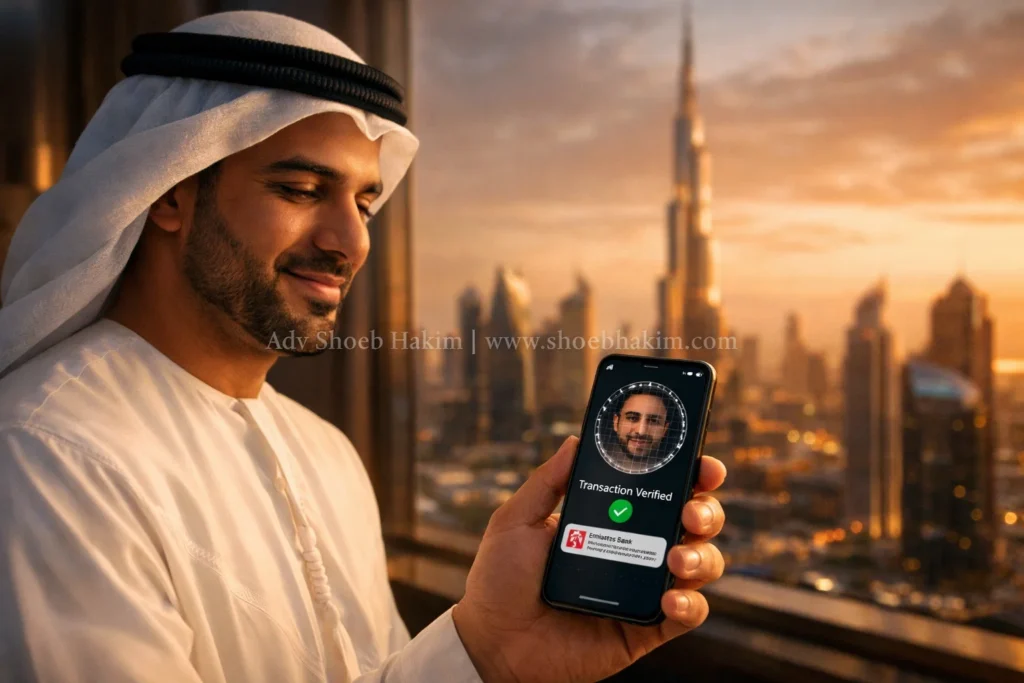
Alt Text: Photo-realistic landscape of biometric authentication on a smartphone illustrating UAE bank SMS OTP phase-out, curated by Adv. Shoeb Hakim.
Title Text: Biometric Authentication Analysis by Adv. Shoeb Hakim
Caption: Exploring the legal complexities of biometric security under global banking frameworks.
Description: This visual asset represents the professional analysis of UAE banking security shifts by Adv. Shoeb Hakim. It highlights the practical application of in-app authentication in modern finance.
- Serial Number: SHOEBHAKIM/JANUARY/WEEK1/030126/003/ADVSHOART+UAEBNK26
Social Media Versions: Multi-Platform Distribution Kits
LinkedIn :
Hook: “Compliance is no longer a cost center; it’s a competitive advantage.”
Post: UAE banks are officially ending SMS OTPs for online shopping on January 6. As someone who has spent 29 years in IT and 15 years in Law, I see this as the inevitable death of a legacy security flaw. SIM-swapping and SS7 interception have made SMS a liability.
CTA: Read my full strategic analysis on ShoebHakim.com.
X (Twitter):
Hook: “BREAKING: The SMS OTP is dying in the UAE. 🧵”
Thread: 1/ Central Bank of the UAE mandates in-app approvals starting Jan 6, 2026. 2/ Why? SIM-swapping and Phishing have cost billions. 3/ Adv Shoeb Hakim explains the “Techno-Legal” shift.
Unified Article JSON-LD: Entity Schema
<script type="application/ld+json">
{
  "@context": "https://schema.org",
  "@graph": [
    {
      "@type": "Person",
      "@id": "https://shoebhakim.com/#person",
      "name": "Adv Shoeb Hakim",
      "jobTitle": "Advocate and Cyber Security Researcher",
      "sameAs": [ "https://shoebhakim.com/"]
    },
    {
      "@type": "AnalysisNewsArticle",
      "@id": "https://shoebhakim.com/uae-banks-end-sms-otp-biometric-authentication-adv-shoeb-hakim#article",
      "headline": "UAE bank to end SMS OTPs: Adv Shoeb Hakim’s Security Analysis",
      "author": { "@id": "https://shoebhakim.com/#person" },
      "datePublished": "2026-01-03",
      "description": "Adv Shoeb Hakim analyzes the UAE's 2026 shift from SMS OTP to biometric in-app authentication to prevent SIM-swapping and fraud."
    }
  ]
}
</script>